Less prominent than the headline-grabbing AI Act or Cyber Resilience Act, the European Product Act and Standardisation Regulation nevertheless deserve close attention. As is often the case in EU product policy, the devil is in the details: the two proposals could significantly reshape the technical and institutional architecture governing access to the Single Market.
Two draft legislative proposals have leaked ahead of their expected presentation by the European Commission:
- a European Standardisation Regulation replacing Regulation (EU) No 1025/2012; and
- a European Product Act consolidating the EU framework for product compliance, accreditation, conformity assessment and market surveillance.
The Product Act would substantially recast the New Legislative Framework by replacing Decision No 768/2008/EC, Regulation (EC) No 765/2008 and Regulation (EU) 2019/1020.
The reform would revisit a regulatory doctrine whose foundations were laid more than forty years ago with the 1985 New Approach and subsequently embedded in the architecture of the Single Market. Under this model, Union legislation establishes essential product requirements, while standards, conformity-assessment bodies and accreditation provide the technical infrastructure for demonstrating compliance.
The two proposals have separate but closely connected functions. The Standardisation Regulation would determine who may develop technical documents supporting Union legislation. The Product Act would give harmonised standards, harmonised deliverables and common specifications practical effects across product compliance, CAB accreditation and conformity assessment.
ESOs would remain central…but no longer exclusive!
CEN, CENELEC and ETSI would remain the recognised European Standardisation Organisations. They would have to be established in the Union and include at least one national standardisation body from every Member State.
The safeguards applying to Commission-requested standards would also be maintained. Decisions on whether to accept or refuse a request, approve the necessary work and adopt, revise or withdraw the resulting document would be reserved to representatives of national standardisation bodies from EU Member States.
The corresponding bodies of Norway, Iceland and Liechtenstein would be covered following the incorporation of the Regulation into the EEA Agreement. Organisations, companies and experts from the United Kingdom or other third countries could continue to participate in technical work, but would not take part in these reserved formal decisions.
For requests concerning Union strategic assets, autonomy or security, the Commission could also restrict participation to entities established and managed in the Union and not controlled by a third country. However, this safeguard would apply only when included in the specific request.
Alternative routes: towards a liberalisation of European standardisation?
The principal structural change is the possibility for the Commission to address a standardisation request to a designated standard development organisation other than an ESO.
Such an organisation would not have to be established in the Union. International private fora and industry consortia would not be expressly excluded.
A designated organisation would need to meet requirements concerning openness, transparency, neutrality, consensus and the participation of Union stakeholders. However, it would not have to include national bodies from every Member State or reserve final decisions to them.
A document developed through this route could subsequently be cited in the Official Journal and support a presumption of conformity. It could therefore produce regulatory effects comparable to those of an ESO document despite being developed under different governance arrangements.
This would introduce a form of liberalisation into a system traditionally organised around three recognised ESOs. It could improve flexibility and access to technical expertise, particularly in rapidly developing sectors. It could also create parallel routes based on different participation, governance, financing and licensing models.
Common specifications: from exception to ordinary regulatory instrument
The Commission could also adopt common specifications directly.
Common specifications already exist in certain sectoral legislation, generally as a fallback where suitable harmonised standards are unavailable. The leaked proposal would make them a permanent horizontal component of the European standardisation framework.
The Commission could use this route following the preliminary consultation of the ESOs where no response was received, an ESO indicated that it did not intend to accept the request or the response was considered unsatisfactory. A common specification could therefore potentially be adopted without a formal standardisation request first being issued to an ESO and failing.
Once adopted, a common specification would provide a presumption of conformity for the requirements it covers. It would therefore move closer to an ordinary regulatory instrument rather than remaining an exceptional solution used only as a last resort.
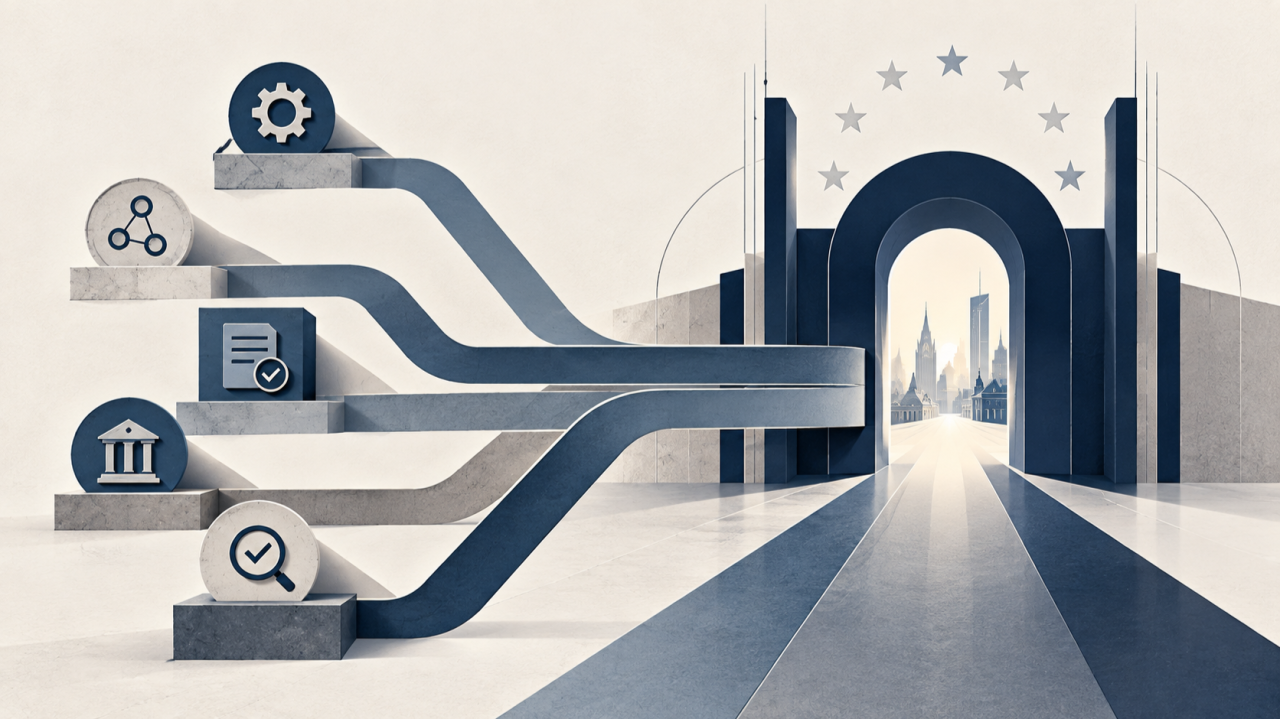
The future framework could consequently rely on three channels: an ESO standard or deliverable, a document developed by a designated SDO or a common specification adopted directly by the Commission.
The effects would extend to CAB accreditation
The Product Act would transmit these technical instruments into accreditation and conformity assessment. Harmonised standards, harmonised deliverables and common specifications could all influence whether a CAB is presumed to meet the applicable competence and independence requirements.
The principle of one national accreditation body per Member State would remain. However, a CAB could apply in another Member State where its domestic body failed to accept, begin or complete the procedure within the announced timetable.
This may help address administrative delays, but it could also encourage accreditation shopping where national bodies differ in speed, expertise or assessment depth. This will be particularly relevant for technically demanding cybersecurity and security evaluations.
Foreign involvement across the assessment chain
The proposal would allow a notified body established in a third country to operate under a mutual-recognition agreement, subject formally to the same requirements as an EU body.
An EU notified body could also rely on foreign subsidiaries, laboratories, experts or subcontractors while retaining responsibility for their work.
Foreign participation does not necessarily constitute interference. It may nevertheless create channels of exposure for source code, cryptographic material, vulnerability information, hardware designs and test results.
The relevant question is therefore not only where a notified body is legally established, but where assessments are performed, who controls the entities involved and whether European authorities can supervise the complete chain in practice.
These developments also raise a broader strategic question: how does opening EU standardisation, accreditation and conformity assessment to a wider range of non-EU organisations and infrastructures fit with the Commission’s efforts to strengthen European technological sovereignty, economic security and control over strategic dependencies?
A broader governance question
The proposals contain genuine safeguards. The ESO route would retain Union establishment, national membership and national decision-making requirements. CABs would face stronger rules on ownership, independence and conflicts of interest.
However, the alternative routes would not reproduce all these safeguards.
The central question is whether standards, technical documents and conformity-assessment results developed through different institutional channels should have comparable effects without equivalent requirements for European participation, accountability and supervision.
The texts currently circulating are leaked drafts and may still change. Nevertheless, they indicate the scale of the reform: Europe is not simply updating individual product rules, but reconsidering parts of the architecture supporting the Single Market for goods.